
Introduction
Many organizations configure NetSuite integrations using an individual employee’s account, role, API token, or external application credentials. While this approach may work during the initial implementation, it introduces a significant business continuity and security risk. If that employee leaves the organization or their account is deactivated, the integration can fail, interrupting critical business processes and requiring emergency troubleshooting.
A NetSuite best practice is to create a dedicated integration user specifically for system-to-system connections. Using a non-human integration account ensures that API authentication, access tokens, and integration ownership remain independent of individual employees. This approach improves security, simplifies administration, reduces downtime, and helps ensure that NetSuite integrations continue operating seamlessly even when employees, consultants, or administrators change roles or leave the organization.
Why Employee-Owned Integrations Are Risky
When an integration is tied to one employee, that person may own:
- NetSuite access tokens
- OAuth authorization
- Integration records
- External application administrator access
- Saved searches
- Scheduled scripts
- Error notifications
- API credentials
If the employee is deactivated, the organization may experience:
- Authentication failures
- Stopped data synchronization
- Missing transactions
- Failed scheduled processes
- Lost administrative access
- Delayed troubleshooting
Integrations should belong to the organization, not one employee.
Step 1: Document the Integration
Before making changes, identify:
- The external application
- The current employee owner
- The NetSuite records being accessed
- The authentication method
- The business process owner
- The technical support owner
- The error-notification recipients
- Any scripts, workflows, or saved searches involved
This helps determine the permissions the new integration user actually needs.
Step 2: Enable the Required NetSuite Features
Navigate to:
Setup > Company > Enable Features > SuiteCloud
Enable only the features required by the integration, such as:
- REST Web Services
- SOAP Web Services
- Token-Based Authentication
- OAuth 2.0
- Server SuiteScript
Confirm the requirements with the external application provider before enabling features.

Step 3: Create a Custom Integration Role
Navigate to:
Setup > Users/Roles > Manage Roles > New
Create a role with a name correlated with the Integration. Add only the permissions required for the integration.
Depending on the application, this may include access to:
- Expense reports
- Employees
- Vendors
- Departments
- Classes
- Locations
- Subsidiaries
- Currencies
- Custom segments
- REST or SOAP web services
Do not assign the Administrator role unless the application specifically requires it and the security team approves the exception.

Step 4: Create the Integration User
Navigate to:
Lists > Employees > Employees > New
Create a clearly named record, such as:
Integration Concur
Use a company-controlled and monitored email address rather than an employee’s personal email.
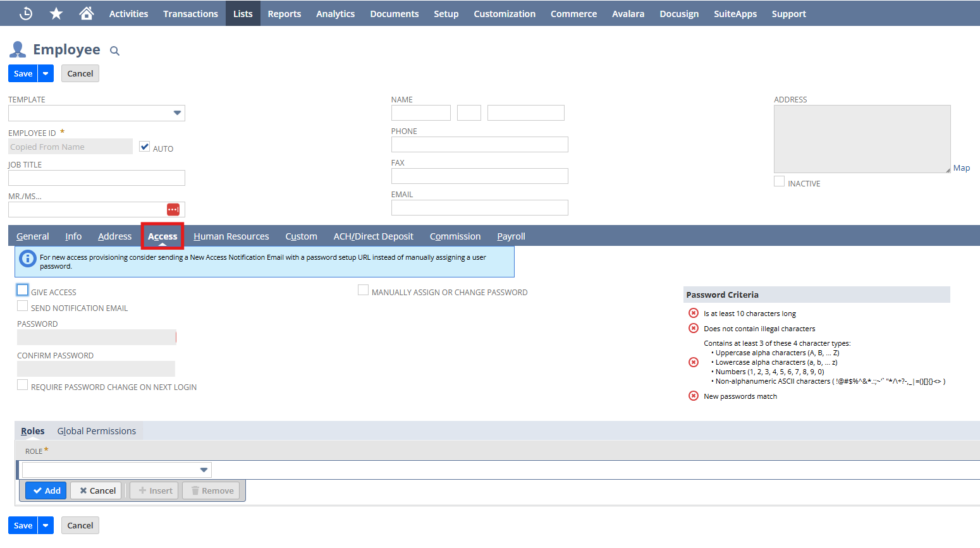
On theAccesstab:
- SelectGive Access.
- Assign the custom integration role.
- Do not assign unnecessary roles.
- Save the employee record.
The account should not be used as a normal shared login.
Step 5: Create the Integration Record
Navigate to:
Setup > Integration > Manage Integrations > New
Enter a descriptive name, such as:
Concur Production Integration
Enable the authentication method required by the application:
- OAuth 2.0
- Token-Based Authentication
Save the integration record and securely store any generated credentials. Do not store tokens, secrets, or passwords in email, spreadsheets, project notes, or screenshots.

Step 6: Create the Access Token
If the integration uses token-based authentication, navigate to:
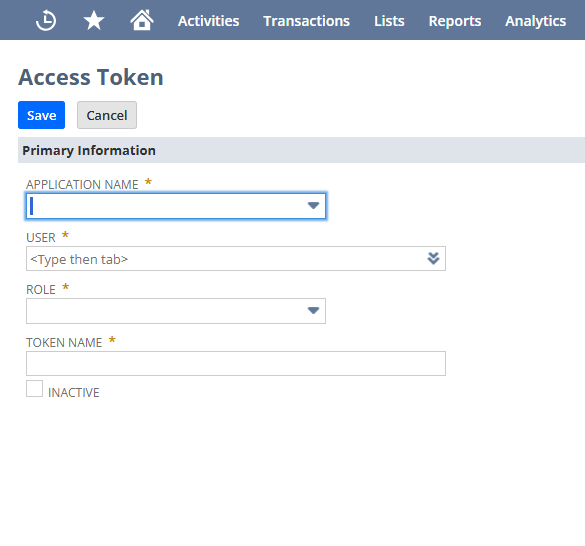
Setup > Users/Roles > Access Tokens > New
Select:
- The integration record
- The dedicated integration user
- The custom integration role
Save the record and securely store the generated:
- Token ID
- Token Secret
Create separate tokens for sandbox and production.
Step 7: Update the External Application
Log in to the applicable external system and replace the former employee-owned connection with the new integration credentials.
Also confirm that the external application has:
- A primary administrator
- A backup administrator
- A shared support contact
- Documented credential ownership
Creating a NetSuite integration user does not eliminate the risk if only one person still controls the external application.
Step 8: Test the Integration
Test the connection in sandbox whenever possible. Do not test only the login. Test the complete business process. Confirm that system activity appears under the new integration user.
Step 9: Document and Monitor the Integration
Maintain documentation that identifies:
- The integration user
- The custom role
- The authentication method
- The business owner
- The technical owner
- The external application administrator
- The credential-storage location
- The error-notification group
- The testing procedure
- The recovery process
- The token-rotation schedule
Do not include actual passwords or tokens in the documentation. Before deactivating an employee, determine whether they own:
- Integration tokens
- OAuth authorizations
- External application administrator access
- API keys
- Certificates
- Scheduled scripts
- Saved searches
- Integration alerts
- Vendor support accounts
A useful offboarding question is:
Does this employee’s account, role, token, email address, or external-system access support an automated process?
This simple review can prevent an unexpected integration outage.

Best Practices
For stronger integration governance:
- Use one identity per major integration.
- Create custom least-privilege roles.
- Keep sandbox and production credentials separate.
- Store credentials in an approved password vault.
- Send errors to a monitored group mailbox.
- Assign both primary and backup owners.
- Review integration users and tokens quarterly.
- Rotate credentials according to company policy.
- Revoke access when an application is retired.
Conclusion
Implementing a dedicated NetSuite integration user is one of the simplest yet most effective ways to improve the reliability, security, and long-term stability of your NetSuite integrations. Critical integrations should never depend on the continued employment of a single administrator, consultant, or employee. Instead, organizations should establish a dedicated, non-human integration account with a custom role, secure API authentication, and clearly documented ownership and maintenance procedures.
This approach is not about creating a shared Administrator account. It is about following NetSuite integration best practices by assigning only the permissions required for each connected application. Whether you’re integrating Concur, Celigo, Salesforce, Shopify, payroll systems, or other third-party applications, a dedicated integration user helps prevent authentication failures, minimizes downtime, strengthens security, and simplifies ongoing administration.
By separating employee access from integration access, organizations can improve business continuity, reduce operational risk, and build a more secure, scalable NetSuite environment that continues to perform reliably as employees, consultants, and business needs evolve.
About Suite Answers That Work – A Rotation Digital Company
Suite Answers That Work is a NetSuite Solutions Provider with more than 30 years of combined experience. We specialize in NetSuite implementation, optimization, integration, rapid project recovery, rescue services, and custom development.
Every business is unique, but with more than 40 NetSuite clients over the last seven years, our consultants have likely seen a similar challenge or helped create a solution for it.
For more information about NetSuite, ERP optimization, or AI-enabled business process improvement, contact us today.